Why a Smart Backup Card Might Be the Best Move for Your Crypto — and How to Do It Right
Okay, so check this out—I’ve been fiddling with hardware wallets, paper backups, and a half-dozen “secure” workflows for years now. My instinct said the gap between convenience and real security in crypto is still too wide. Something felt off about relying on handwritten seeds or a thumb drive. Really? Yes. The smart backup card idea hooks both simplicity and resilience. It’s tangible. You can carry it in a wallet. You can tuck it into a safe deposit box. But it’s not magic; it’s a design choice with trade-offs, and those trade-offs matter if you hold multiple currencies or want easy recovery for a friend or family member.
Whoa! Brief aside—I’m biased toward hardware-first solutions. I’m an engineer at heart, though I enjoy the practical life-hacks more. Initially I thought a single “cold” device would cover everything. Then reality hit: diverse chains, different signing schemes, and human factors mean a one-size approach breaks fast. On one hand, smart cards solve many problems. On the other hand, they introduce new operational risks if you ignore simple procedures. Let’s walk through how to pick, use, and back up a smart-card-based system that actually works in the messy real world.
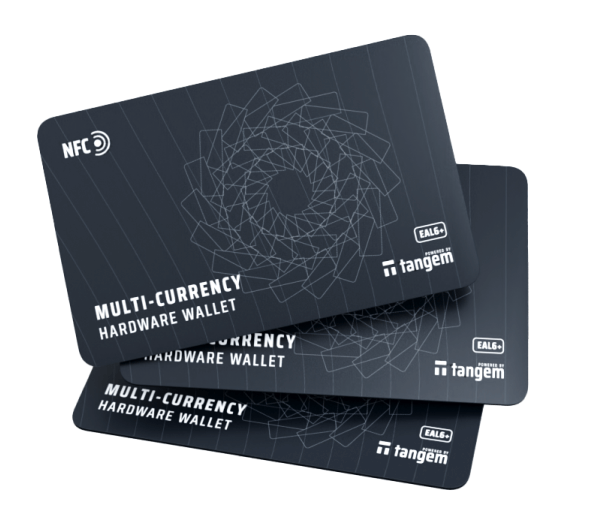
Why smart backup cards make sense (and where they don’t)
Short answer: they’re physical, compact, and user-friendly. Short. But also nuanced. Most hardware wallets are bulky or require cables. Paper seeds are fragile. A laminated list? Nope. Smart cards—cards that hold private keys in a secure element—offer a middle path: portability with tamper-resistant hardware. They’re like carrying a credit card that happens to be your vault.
My first impression was enthusiasm. Then I dug into interoperability: not all chains treat keys the same. Some require SegWit/PSBT workflows, others need contract interactions, and some chains demand offline messaging for signatures. So, somethin’ to keep in mind—smart cards that natively support multi-currency signing save you friction. If you rely on a bridge or intermediary service to “translate” signatures, you’re back to trusting extra parties.
Here’s what bugs me about some cheap “backup card” solutions: they either store plain seeds (dangerous) or they force you into a single-vendor ecosystem. That’s a tradeoff I don’t like. The better cards use standards, keep private keys in a secure element, and let apps talk to them over NFC or BLE without ever exposing raw keys. That way, even if your phone is compromised, the private key doesn’t leave the card. Hmm… neat, right? But there’s more.
Key features to evaluate for multi-currency use
Okay—practical checklist time. Don’t skim this. I’ll be blunt: if your card doesn’t meet at least these criteria, don’t trust it for significant funds.
- Secure element with certified randomness and key isolation. No exceptions.
- Support for multiple signature schemes (secp256k1, ed25519, etc.) so you can handle Bitcoin, Ethereum, Solana, etc.
- Open standards and a public API or clear SDK. Closed black boxes are red flags.
- Backup/backup-share workflows that don’t reveal the private key (Shamir-like or split-key approaches are nice).
- Offline signing capability and straightforward verification of signed data.
- Reasonable UX for non-technical users—apps that guide confirmations and display transaction summaries.
On the multi-currency note: some very small teams claim “support” for dozens of coins, but often it’s superficial—token transfers via a custodial relay rather than native signature support. That’s not the same. If you care about sovereignty, look for native signing, not wrappers. I’m not 100% sure about every product out there, but that distinction saved me from a nasty surprise once.
Backup cards vs. other backup strategies
Think in terms of threat models. Who are you defending against? Loss, theft, hardware failure, coercion, or just plain forgetfulness?
Paper seed: resilient to digital attack but fragile (fire, water, handwriting errors). Hardware wallet: secure key storage but sometimes inconvenient for everyday use. Backup card: portable and usable, but if you lose it, someone with access and some time could try to abuse it—unless you add passphrases or split the backup.
One effective hybrid: use a smart backup card as a daily-carry cold signer for small amounts, keep the main vault in a full-featured hardware device, and store a split backup (Shamir or multi-card approach) in geographically separated locations. That combo balances convenience with catastrophic failure protection.
On a practical note—I once used a card-based backup while traveling cross-country. It was slick. I authorized micro-transactions quickly with my phone via NFC. But I also realized I needed clearer step-by-step instructions for a trusted relative in case I was indisposed. Don’t assume your sibling can follow a 12-step recovery flow; simplify it ahead of time.
Operational tips that actually work
Here’s a small playbook—short, actionable, and tested in the field (by me and by a few friends, at least).
- Label but don’t label. Use a faint code on the card’s sleeve or a hint not obvious to strangers. Don’t write “crypto” on your card!
- Use a passphrase (BIP39 passphrase) in addition to the card. Treat the passphrase like a second factor. If you lose the card, the passphrase keeps funds safe. If you forget the passphrase, funds are lost—so record it cleverly.
- Consider creating two backup cards and splitting risk: one you carry, one you stash in a safe place.
- Practice recovery annually. Seriously. Run a mock restore to a clean device so you know the steps and the timing.
- Document access instructions for a trusted person with clear escalation paths (not full keys, but how to find them). This is governance for your personal estate planning.
One more: avoid single-channel backups. If your card depends on an app that stores metadata, ensure that metadata can be reconstructed or is portable. Apps come and go; exports get deprecated. Keep formats that are openly documented.
How to evaluate vendors and the tech behind the card
I’m going to be blunt. Vendors will market neat features. Focus on these technical signals instead:
- Has the firmware been third-party audited? Look for public audit reports.
- Is the secure element from a reputable chipmaker? Which one?
- Are cryptographic primitives public and standard? Or proprietary black-box crypto?
- Is there a developer community or SDK? Active contributors matter.
- How do they handle firmware updates? Secure update channels are essential.
Oh—and customer support. This is underrated. I once bet on a slick UI and then got ghosted when I needed help with a recovery edge-case. Don’t do that.
Where to start if you want a practical pick
If you want to test the idea without committing, get a card that explicitly supports multi-currency signing and has a minimal required app. Try sending and receiving small amounts first. Learn the confirmation screens. Check how the card indicates what you’re signing—do the prompts show recipient address, amount, chain ID? If not, it’s risky.
Another practical resource is the broader ecosystem documentation—some vendors maintain solid guides for setups and shared recovery workflows. One product I frequently reference in conversation is the tangem wallet family, which packs the smart-card concept into a user-friendly form factor and supports several chains natively. I’m not sponsored. It’s just a useful example of the tradeoffs in real devices: convenience, hardware-grade security, and multi-chain reach.
Common questions people actually ask
Can a smart backup card be cloned?
Short answer: not easily. Secure elements are designed to prevent key extraction or cloning. However, if the card’s firmware or supply chain is compromised, cloning risk increases. Treat cards like any physical security: keep them safe, and verify vendor integrity.
What happens if the card is damaged?
If you used a single card without a passphrase and didn’t split the backup, damage can be catastrophic. That’s why redundancy matters. With a passphrase, damage only matters if you lose both card and passphrase. So plan for multiple failure modes.
Are smart cards good for long-term storage?
Yes, for many people. They are durable and often rated for long shelf life. But long-term equals decades sometimes—so choose cards with stable vendor support and exportable, well-documented formats so a future device can read your backup data.
Alright—final thought. I started this with skepticism and ended with cautious optimism. The smart backup card model isn’t a panacea, but for many users it hits a sweet spot: more secure than paper and more convenient than bulky hardware. If you combine one with good operational practices—passphrases, redundancy, periodic recovery tests—you get a system that is both usable day-to-day and robust against serious failure.
I’m biased, sure. But practical experience matters more than theory here. Try it, test it, and make sure a trusted person knows the recovery story. You’ll sleep better. Or at least, you’ll sleep more realistically—because life happens, and crypto doesn’t forgive sloppy backups.